Cybersecurity for Financial Services
NetMonkeys is a reliable IT company delivering cybersecurity services to financial organsiations for the last 20 years. 40+ Finance startups across the UK trust us to secure their technology insfrastructure


Commercial Summary: Financial Cybersecurity Services
NetMonkeys provides outsourced, board-ready cybersecurity solutions for financial services firms across the UK. We replace fragmented IT setups with an integrated security framework: 24/7 UK SOC threat hunting, Managed EDR, Zero Trust identity hardening, and direct mapping against FCA Operational Resilience, PRA, and UK GDPR regulations.
What our cybersecurity in financial services entails & actually includes
A comprehensive financial cybersecurity programme is not an off-the-shelf antivirus package—it is an active, multi-layered defence system covering real-time threat response, identity governance, and continuous regulatory evidence generation and thas what we deliver to our clients.
- 24/7/365 UK-based SOC telemetry and active threat hunting
- Managed EDR with automated sub-10-minute threat isolation
- FCA, DORA, and UK GDPR audit-ready documentation & logging
- AI-driven email filtering to stop Wire Fraud and Impersonation (BEC)
- Zero Trust identity architecture with conditional access MFA
- Immutable, write-once-read-many (WORM) cloud backups
- Full lifecycle management for Cyber Essentials Plus certification
- Scoped penetration testing and automated vulnerability assessments
- Third-party and supply chain cybersecurity risk assessments
- Documented 72-hour ICO & FCA incident response frameworks
Financial cybersecurity services from NetMonkeys
Our financial cybersecurity services are built as one coordinated programme rather than a stack of disconnected tools bought separately and never properly integrated. Explore our core commercial capabilities below.
Managed Detection & Response (MDR)
Continuous monitoring by our UK security analysts for signs of a developing incident—unusual login activity, attempts to exfiltrate client records, or lateral movement between systems.
→ Explore EDR ServicesPenetration Testing & Auditing
Independent, evidence-based testing of your network and client portals. We run scoped penetration tests simulating realistic attacks, providing technical reports and board-level risk summaries.
→ Explore Pen TestingCompliance & Certification
We support firms working towards Cyber Essentials, Cyber Essentials Plus, and ISO 27001, translating technical controls into the evidence regulators and institutional investors expect to see.
→ Explore CertificationManaged Firewall & Network Defense
Proper network architecture and micro-segmentation that prevents a breach on a single workstation from spreading freely to systems holding client capital or sensitive deal pipelines.
→ Explore FirewallsSecuring Hybrid Financial Teams
Device encryption, structured patch management, and behavioural threat detection across every device your team uses to access client platforms from home, the office, or between meetings.
→ Explore Endpoint SecurityFinancial IT Support Integration
Seamlessly blending infrastructure support with active cyber defense. We eliminate the friction of managing separate IT and security vendors, reducing vulnerabilities across the board.
→ Explore Financial ITBenefits of cybersecurity for financial services
The importance of cybersecurity in financial services is directly measurable on your balance sheet and operating stability. A robust cybersecurity programme delivers significant commercial advantages:
FCA & Regulatory Protection
Avoid punitive fines, enforcement actions, and mandatory audits by embedding continuous compliance and operational resilience into your day-to-day operations.
Cyber Insurance Optimization
Insurers now demand proof of active MFA, EDR, and immutable backups. Our verified controls enable firms to secure lower premiums and avoid coverage denial.
Institutional Client Trust
Win more business by effortlessly passing vendor due diligence questionnaires from institutional partners, lenders, and high-net-worth clients.
Zero Transaction Downtime
Trading and payment processes never stop. Isolated containment and high-availability architecture protect your fee-earners during critical market windows.
Elimination of Wire Fraud
Advanced DMARC and AI email security stop payment redirection scams before a single fraudulent instruction can be executed by your accounts team.
Predictable OPEX Model
Replace the volatile, £300k+ annual expense of building an internal SOC with fixed, scalable monthly pricing that adapts as your firm expands.
Why financial services choose our financial cybersecurity services
Our approach goes beyond merely ticking compliance boxes. We engineer resilient IT infrastructures tailored specifically to the high-stakes environment of UK finance, ensuring your operations remain impenetrable, compliant, and continuously available.
A Partnership built on security.
As a reputable security company, we focus on making sure we protect UK businesses from local or off-shore attacks.
We are trusted by 40+ UK-based financial corporations, startups and SMEs.
Immutable Data Sovereignty
Guaranteed UK-only data residency for all backups and cloud storage, eliminating cross-border compliance violations.
Rapid Incident Containment
Automated isolation protocols engineered to stop active ransomware threats in milliseconds, not hours.
Frictionless Auditing
Pre-mapped compliance reporting that turns complex FCA and Cyber Essentials Plus audits into a straightforward process.
Board-Level Risk Reporting
We translate deep technical metrics into clear, commercial risk assessments tailored directly for your board of directors.
How to choose a cybersecurity provider for your financial firm
Selecting the right Managed Security Service Provider (MSSP) is one of the most critical decisions a financial director will make. When evaluating potential cybersecurity partners, ensure they satisfy these core requirements:
1. Genuine Financial Regulatory Track Record
Ask how they map technical controls to FCA operational resilience rules, DORA, and GDPR. A generic IT provider will offer standard antivirus; a financial specialist will deliver audit-ready evidence logs.
2. 100% UK-Based Security Operations
Verify where their security analysts reside. To maintain strict data sovereignty and prevent cross-border compliance violations, all telemetry and incident responses should be handled within the UK.
3. Enforceable SLA for Threat Containment
In financial services, a ticket response time is meaningless if ransomware is already spreading. Require a contractual commitment for immediate, automated endpoint containment.
4. Holistic IT & Security Alignment
Having separate vendors for general IT and cybersecurity creates finger-pointing during an outage. Seek a partner capable of managing the entire infrastructure securely.
5. Cyber Essentials Plus Accreditation
Ensure the provider holds Cyber Essentials Plus themselves and possesses certified lead auditors who can guide your internal team to certification without friction.
6. Transparent, Headcount-Based Scoping
Avoid providers who push complex hardware leases. Look for predictable, per-seat monthly contracts that allow your firm to scale flexibly without penalising growth.
The threats financial services firms actually face
Financial firms see a specific and fairly consistent pattern of attacks, shaped by what attackers know they can extract from the sector.
Business Email Compromise (BEC)
Aimed at redirecting payment instructions by impersonating a client, solicitor, or supplier. It remains the most damaging financial attack vector.
Credential Harvesting
Attackers target advisor portals and M365 tenants to steal session tokens, particularly where firms have not enforced strong, conditional MFA.
AI-Generated Social Engineering
Increasingly convincing generative-AI phishing emails closely mimic legitimate correspondence, bypassing basic staff intuition.
Ransomware protection and stopping email compromise with our cybersecurity in financial services
Downtime in a financial services business stops transactions mid-process, delays client onboarding, disrupts regulatory reporting deadlines, and prevents firms from meeting contractual obligations.
Our ransomware defences combine endpoint detection, network micro-segmentation, and immutable cloud backups designed specifically to contain an attack in seconds and allow full data recovery without paying a ransom.
Zero Trust and identity access controls: Core cybersecurity for financial services
In modern cybersecurity in financial services, the perimeter is no longer the physical office—it is the user's identity. We implement Zero Trust models requiring continuous verification.
By enforcing role-based access controls, multi-factor authentication across all critical systems, and privileged access management (PIM), you can produce a clear, evidenced answer when an auditor asks who can access client data.
Cybersecurity for payment processing and financial transactions
For financial organisations handling high-volume transactions or sensitive payment data, system latency or breach is catastrophic. We architect resilient, high-availability IT infrastructures designed specifically to protect secure payment processing and continuous trading environments.
High-Availability Architecture
Redundant network pathways and load-balanced server environments ensure your transaction processing systems never experience a single point of failure.
Secure Data Transmission
Implementing advanced encryption protocols (TLS 1.3) and secure VPN tunnels to guarantee the absolute confidentiality of transactional data in transit.
PCI-DSS Compliance Support
Continuous monitoring, vulnerability management, and network segmentation to ensure cardholder data processing adheres to global compliance criteria.
Cybersecurity solutions in financial services by sub-sector
The threat profile and regulatory pressure vary significantly across disciplines. We align our cybersecurity configurations to the operational demands of your specific sector.
Banks & Specialist Lenders
Securing payment systems, controlling access around underwriting portals, and protecting applicant financial data from exfiltration.
Insurance Providers
Tailored security around claims systems—strong access controls, encryption of policyholder records, and anomaly detection.
Wealth Managers & IFAs
Verification protocols to stop client impersonation fraud, alongside hardened cloud storage for confidential investment portfolios.
FinTech & Payment Firms
Security architecture reviews, PCI DSS alignment, automated cloud security controls, and third-party penetration testing.
Why standard IT support fails financial services
Generic IT support is fundamentally reactive—designed to fix a printer or reset a password. Financial services cybersecurity must be relentlessly proactive.
The Reactive Gap
Standard IT waits for you to log a ticket when a system fails. We actively monitor your network 24/7, identifying anomalous behaviour and isolating threats before they trigger an outage.
Compliance Blind Spots
Generalist providers often lack an understanding of FCA operational resilience and DORA requirements, leaving your firm exposed to regulatory fines and audit failures.
Basic Defenses
Basic antivirus cannot defend against targeted ransomware campaigns affecting wealth managers and PE firms. We deploy true Managed Detection and Response (MDR).
Our SOC services for financial companies
Managing a Security Operations Centre (SOC) internally requires hiring for multiple high-salary disciplines—threat hunters, compliance officers, cloud architects. Outsourcing provides an entire team of specialists for a predictable fraction of the cost.
| Capability | Outsourced MSSP (NetMonkeys) | In-house Security Hire |
|---|---|---|
| 24/7/365 Real-Time Telemetry | ✓ Continuous UK-based monitoring | ✗ Limited to business hours |
| Automated Threat Disruption | ✓ Sub-minute ransomware isolation | ✗ Manual ticket-based response |
| Regulatory Evidence Logging | ✓ Automated FCA-compliant reporting | ✗ Ad-hoc log compilation |
| Proactive Vulnerability Scanning | ✓ Weekly automated sweeps & patching | ✗ Annual or bi-annual checks |
| Specialised Finance Threat Intel | ✓ Sector-specific attack pattern matching | ✗ Generic IT alerts |
Discover financial services cybersecurity built around your firm
NetMonkeys has spent years supporting regulated businesses across the UK, which means we understand the practical reality of running a cybersecurity programme alongside genuine FCA obligations. Discover financial services cybersecurity that's genuinely shaped around how your firm operates.
Explore Our Financial IT ServicesA zero-downtime cybersecurity migration framework for finance
Upgrading your security posture shouldn't disrupt your trading floor or expose client data during the handover. We utilize a phased, shadow-deployment methodology that ensures absolute continuity.
Silent Discovery & Risk Mapping
We deploy read-only discovery agents to map your existing data flows, identifying shadow IT and vulnerabilities without alerting bad actors or disrupting current operations.
Parallel Architecture Build
Our engineers construct your hardened cloud environment and Zero Trust policies alongside your existing infrastructure, fully testing configurations prior to any live cutover.
Staged Vendor Offboarding
We professionally manage the separation from your legacy IT provider, securely revoking their access tokens and transferring administrative control seamlessly.
Weekend Cutover & Validation
Critical DNS, EDR, and firewall switches are executed over the weekend. Our team performs extensive penetration testing on the new perimeter before Monday morning.
Hypercare & Continuous SOC Activation
Your firm enters a designated hypercare period with priority support, while our 24/7 SOC officially takes over active threat monitoring.
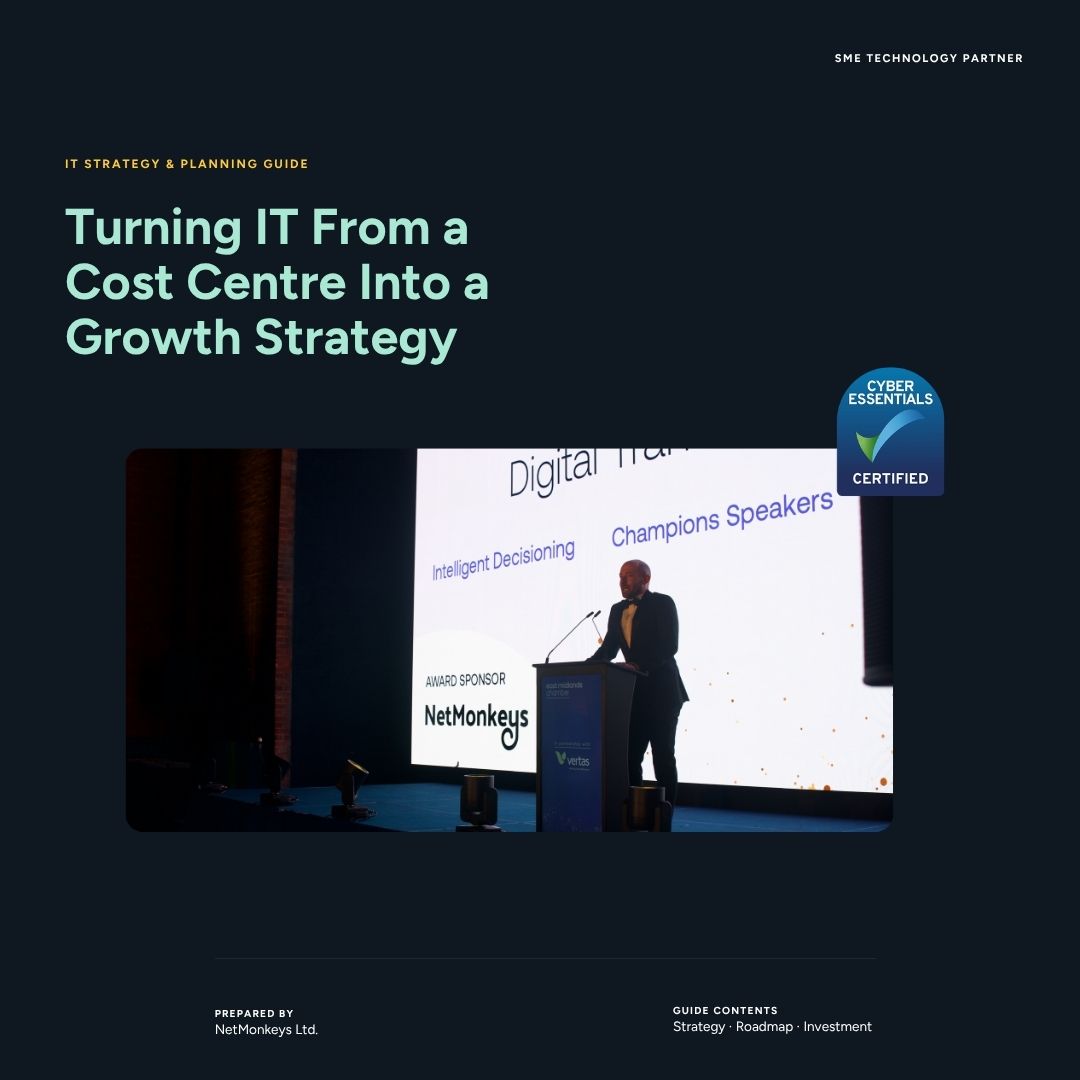
Cybersecurity and IT Guide for Finance Businesses
For financial organisations, navigating the intersection of technology and security is a board-level priority. Moving away from a reactive IT model towards a proactive, structured strategy is critical to safeguarding client assets and meeting strict FCA and DORA obligations.
Download our exclusive guide to discover how to align your digital infrastructure and cyber defences with your firm's commercial goals. We detail exactly how to forecast your hardware lifecycles, conduct rigorous security audits, and permanently eliminate the risks associated with technical debt.
Download the Free Guide"NetMonkeys didn't just take over our IT; they restructured our entire security posture to satisfy our strict FCA obligations, without slowing down our traders. Their understanding of the financial sector's need for zero-downtime is unmatched."
London-based Wealth Management Firm
Our Case Studies
Discover how we help businesses transform their operations, secure their infrastructure, and migrate to modern cloud environments seamlessly.
Cloud Success with Microsoft 365 Support for Invopak
Read how we modernised Invopak's infrastructure by migrating them to Microsoft 365, enhancing team collaboration and operational efficiency across multiple sites.

Guiding TEPS' Strategic Migration to Microsoft 365 & SharePoint
Explore our step-by-step approach to migrating TEPS' legacy systems to SharePoint Online, securing their data and streamlining document management.
Trusted by UK companies for financial cybersecurity
We take pride in delivering robust, high-performance security operations that our clients can rely on without question. Read firsthand experiences from financial organisations that have entrusted their data protection and IT infrastructure to NetMonkeys.
Great IT support from Netmonkeys Ltd. Their quick response time really stands out issues get resolved fast with minimal disruption.
NetMonkeys are truly at the top of the tree when it comes to supporting and guiding on IT issues and future proofing.
Netmonkeys provides a strong range of services across IT support, networking, cybersecurity, and proactive system...
Cybersecurity articles for UK organisations
Practical advice, compliance frameworks, and step-by-step guides written by NetMonkeys senior security engineers to help UK businesses navigate digital threats, compliance audits, and cyber risk.
How to Choose an IT Support Company: A Practical Guide
Key criteria, SLA checks, and critical questions UK financial businesses must evaluate before hiring or switching managed service providers.
Read Full Guide → CybersecurityWhat is Endpoint Detection & Response (EDR)?
Why traditional antivirus is no longer sufficient and how modern EDR actively detects, isolates, and remediates sophisticated ransomware.
Read Full Guide → ComplianceCyber Essentials vs Cyber Essentials Plus
A detailed breakdown of both standards, auditing requirements, and why financial firms need technical verification for regulatory compliance.
Read Full Guide → Microsoft 365How to Enable 2FA in Microsoft 365: Step-by-Step
Enforce multi-factor authentication across your organisation with conditional access policies and Microsoft Authenticator setup.
Read Full Guide → Security AuditsWhat is a Vulnerability Scan? (Nessus Network Guide)
Discover how regular automated scanning uncovers missing patches, outdated ports, and network exposures before attackers exploit them.
Read Full Guide →Supporting financial services firms with cybersecurity across the UK
While our SOC monitors your network continuously from our headquarters, we provide rapid on-site dispatch across major financial hubs. Whether you need an emergency incident response, a compliance audit, or hands-on infrastructure support, our engineers are deployed locally.
Cybersecurity in Financial Services FAQs
Direct answers to the questions financial firms ask us regarding security, risk, and compliance.
Do you provide cybersecurity for financial services firms facing FCA audits?
Yes. We implement the technical controls, data retention policies, and security measures necessary to satisfy FCA guidelines and strict GDPR requirements for handling financial data.
How do your financial cybersecurity services protect us against invoice fraud?
We deploy advanced email security, including DMARC/DKIM/SPF enforcement and AI-driven impersonation detection, which actively flags and blocks fraudulent payment requests and phishing attempts.
Can you secure our legacy financial software?
Yes. We provide cybersecurity solutions for financial services using legacy applications, ensuring they remain segmented and protected while planning safe migrations to modern cloud alternatives.
Are your security engineers based in the UK?
100% of our SOC and senior engineers are based in the UK. We do not outsource our security monitoring to offshore call centres, ensuring clear communication and strict data sovereignty.
What happens if our trading floor is targeted by ransomware?
Our managed EDR automatically isolates the infected device from the network to prevent lateral movement. Simultaneously, our guaranteed 15-minute response SLA ensures our engineers begin rapid remediation immediately.
How do you manage Cyber Essentials Plus for our firm?
We handle the entire certification process end-to-end. We configure firewalls, enforce endpoint patch policies, secure access controls, conduct pre-audit vulnerability scans, and liaise directly with the external assessor.
How does NetMonkeys ensure complete UK data sovereignty for financial records?
We configure all cloud tenants, including Microsoft 365 and Azure Landing Zones, with geo-fencing policies locked exclusively to UK South and UK West data regions, ensuring strict adherence to UK data protection legislation.
Do you offer cybersecurity solutions in financial services scaling rapidly?
Yes, our pay-as-you-grow model allows fintechs and growing wealth managers to adopt enterprise-grade protection that scales linearly with their headcount, ensuring predictable monthly costs.
Start with a no-obligation security review
Ensure your firm's data is secure, compliant, and always accessible. Contact NetMonkeys for a confidential discussion about your security posture.